


Secure your embedded devices throughout their lifecycle
Tria CVE helps industrial OEMs identify, assess and manage vulnerabilities throughout the lifecycle of embedded products.
Built for long-lived Linux-based devices, Tria CVE reduces vulnerability management effort, supports Cyber Resilience Act (CRA) processes, and helps security teams focus on the risks that actually matter.
Tria CVE is free to use for Tria customers.
Stop spending engineering time manually correlating vulnerability databases, software inventories and patch information.
Establish a structured vulnerability management process with reporting, documentation and audit capabilities that support CRA compliance activities.
Manage vulnerabilities across multiple software platforms, projects and product generations with a single tool.
Maintain full ownership of sensitive product security information while integrating vulnerability management into CI workflows and security processes.
Effective vulnerability management starts with understanding exactly what software is running on your products.
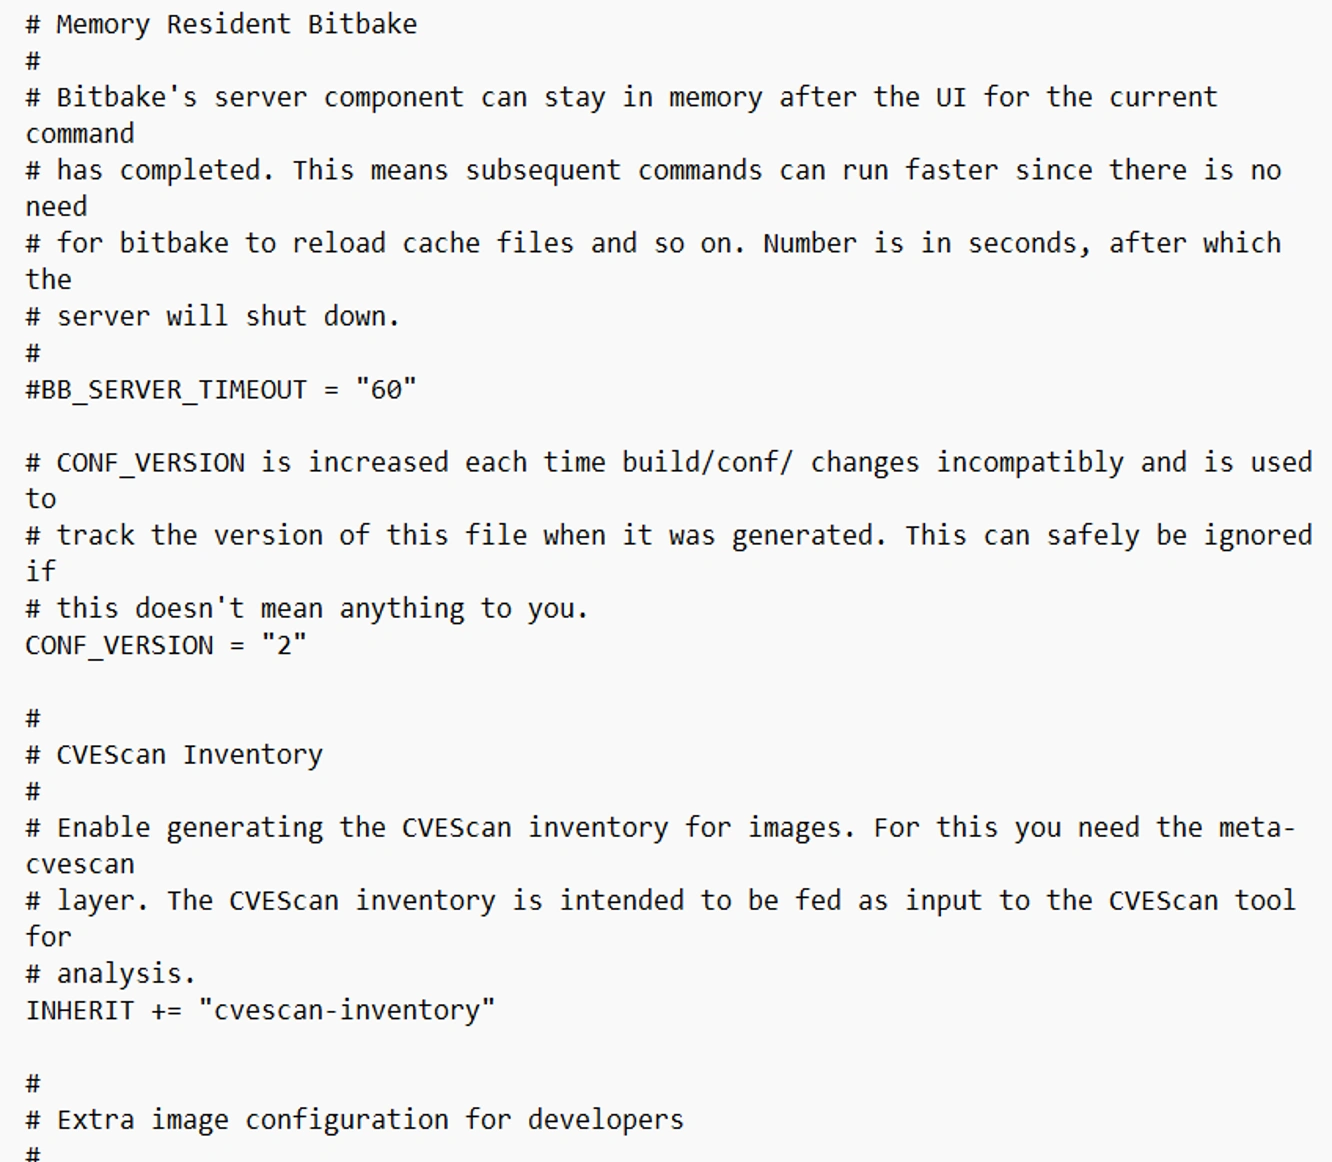
Tria CVE generates and manages Software Bills of Materials (SBOMs) for Yocto, Buildroot and Zephyr-based projects, providing the foundation for vulnerability tracking and security reporting.
Our vulnerability management software also supports industry-standard formats including SPDX and CycloneDX, enabling CVE monitoring across Linux, containers, applications and RTOS environments.
Tria CVE analyzes SBOM data and correlates it with multiple vulnerability sources, including public databases such as NVD, Ubuntu CVE Tracker and OSV.
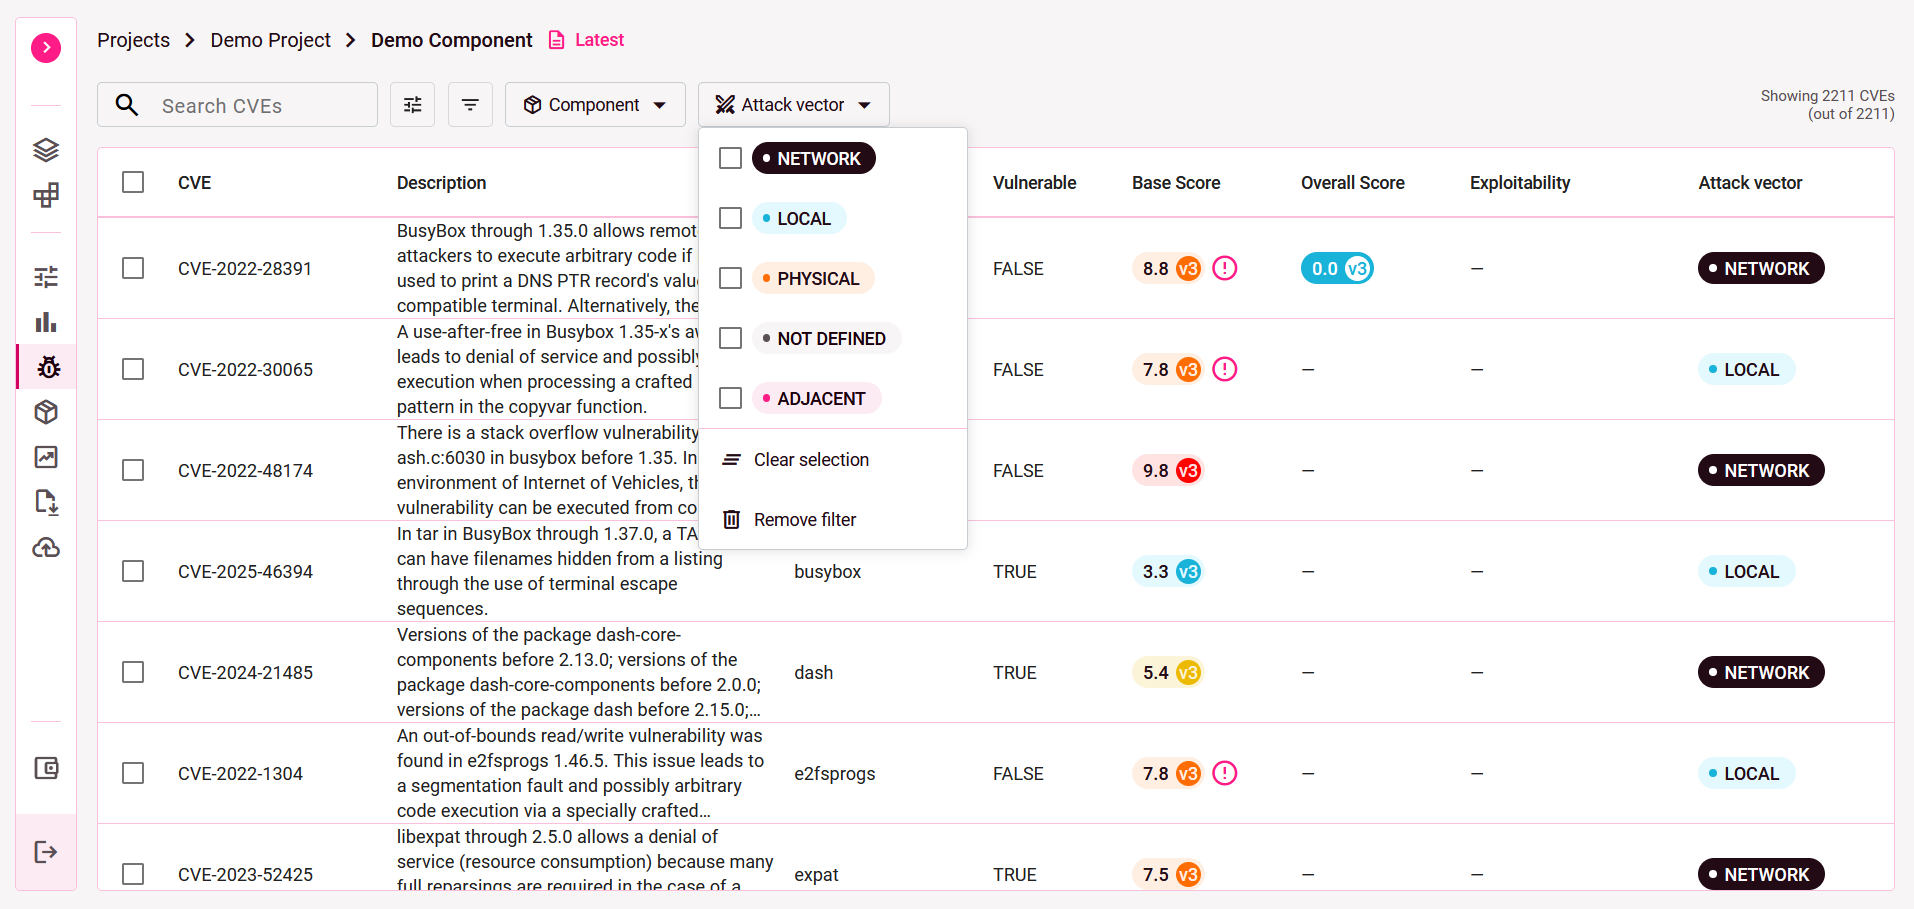
By matching versions and component metadata, the vulnerability management software builds a prioritized inventory of vulnerabilities relevant to your specific product configuration.
Most vulnerability scanners generate long lists of potential issues.
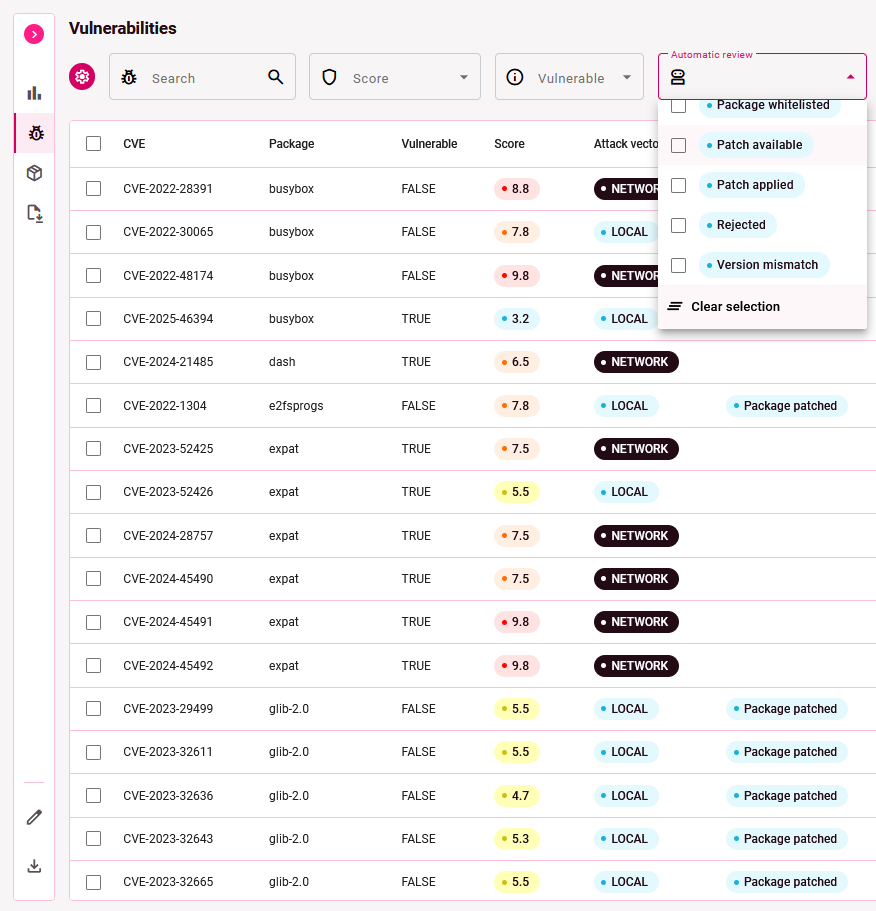
Tria CVE goes further by analyzing Linux kernel configurations, affected source code and applied patches, including backported fixes.
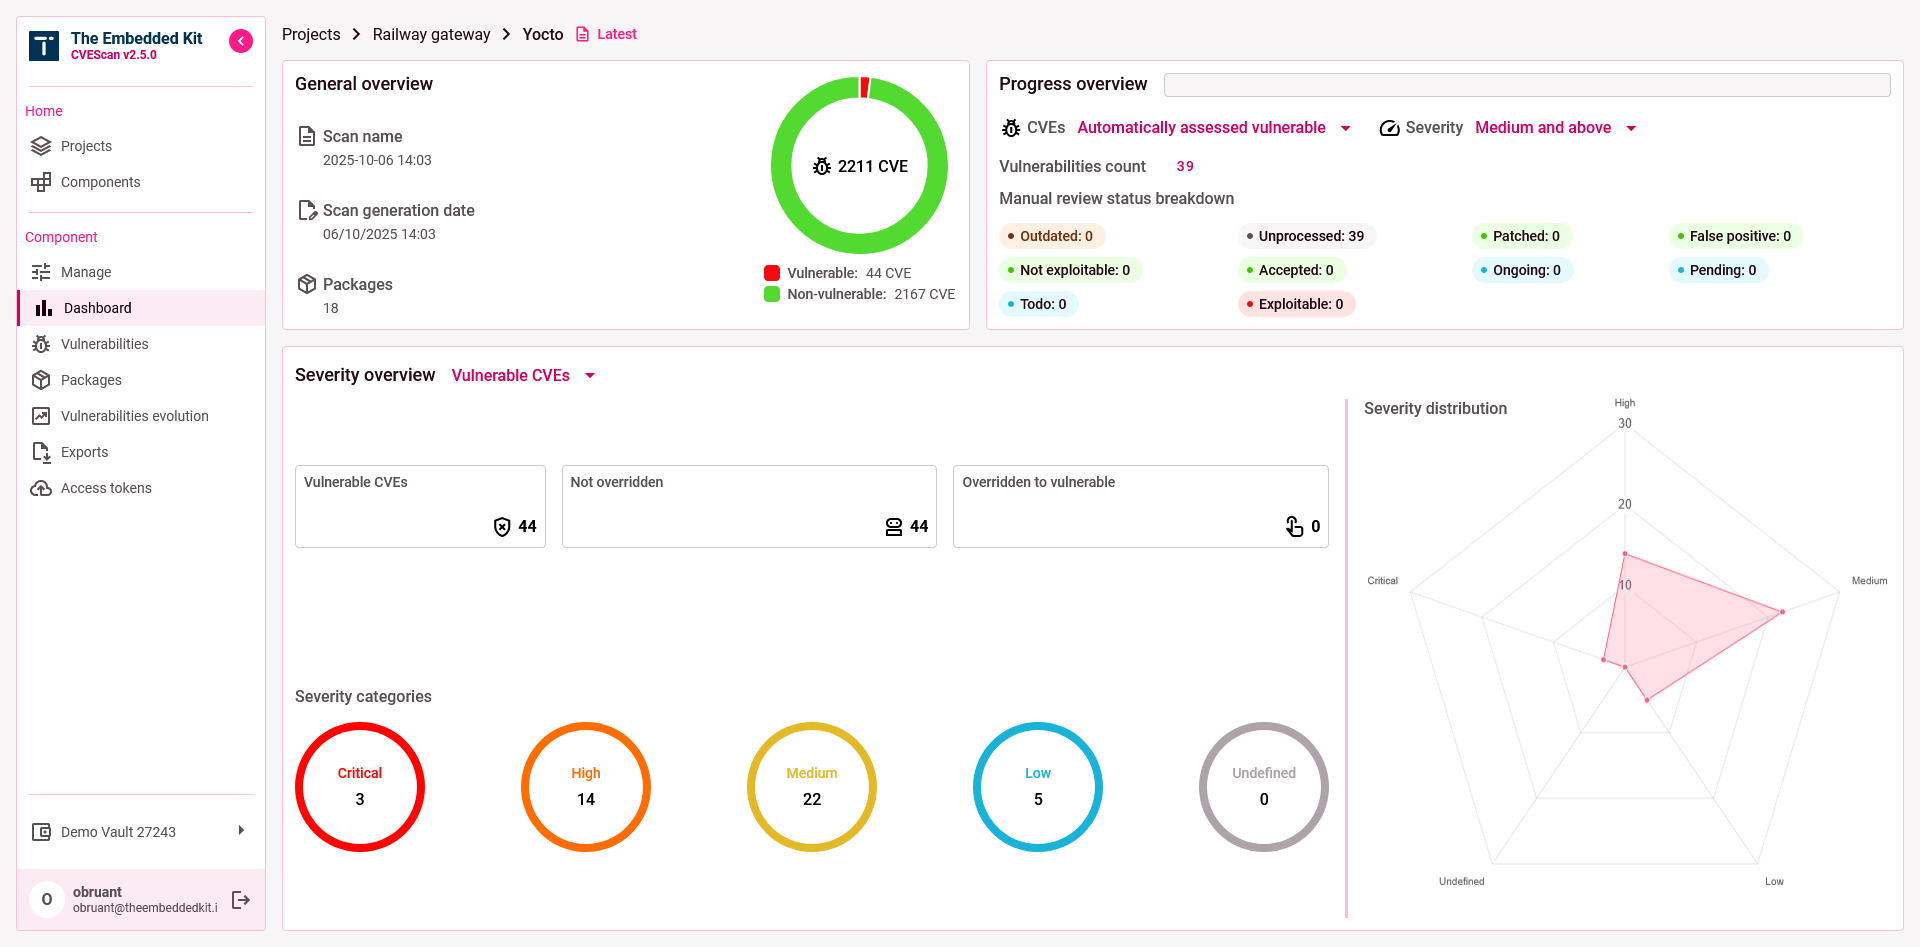
It generates visual reports with scoring and detailed information to determine which vulnerabilities pose a risk, and how to address them effectively.
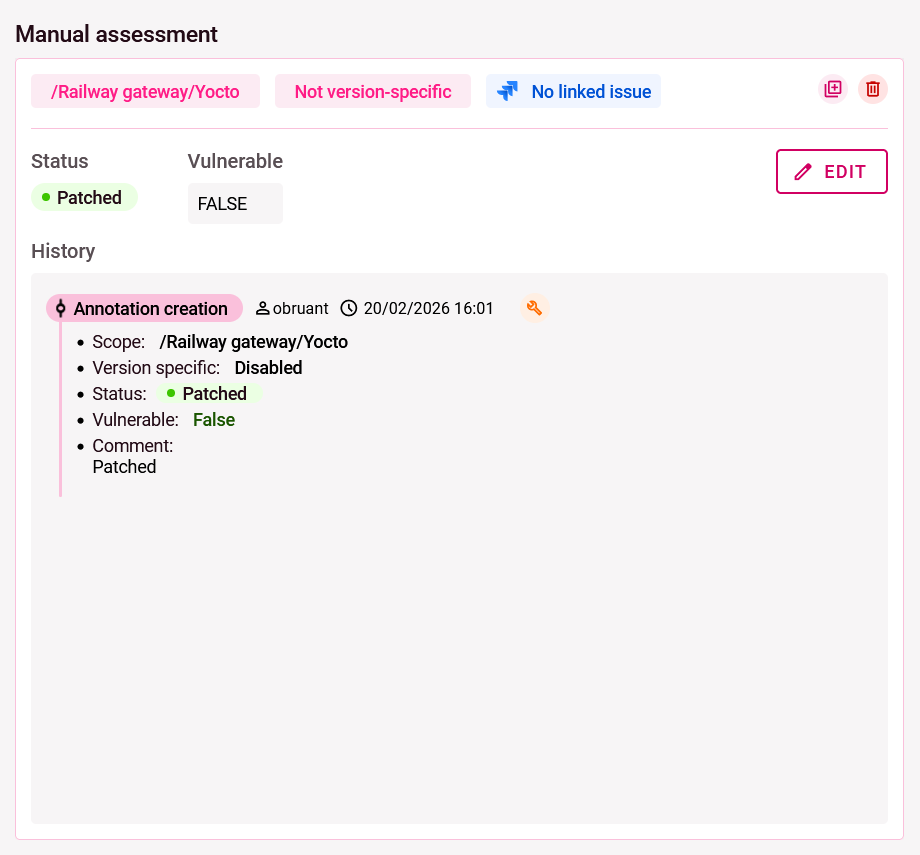
Our CVE management tool records vulnerability assessments, remediation actions and manual annotations with timestamps and status tracking, creating a complete audit trail of security activities.
Dashboards and monitoring views help teams track evolving risks while supporting internal reviews, customer requirements and regulatory audits.
Control access to vulnerability information across teams and departments.
Tria CVE provides flexible user, role and permission management to ensure sensitive security information is available only to authorized stakeholders.
Track security activities through centralized dashboards, document decisions through annotations and comments, and export detailed reports for customers, auditors and internal stakeholders.
Maintain visibility across engineering, security and compliance teams with a consistent source of truth.
The Cyber Resilience Act (CRA) requires manufacturers to implement vulnerability management processes throughout the supported lifetime of their products.
Tria CVE helps support these activities through:
If your team prefers to focus on product innovation rather than operating system maintenance, Tria provides a SLA-backed vulnerability monitoring and maintenance service called SuperCare for your Tria platform.
Our experts continuously monitor vulnerabilities, analyze product impact and support remediation activities while giving you access to Tria CVE for reporting and traceability.
Focus on building product features. We’ll help manage your platform security.
A railway equipment manufacturer needed to maintain the security of a Linux-based passenger information and control system expected to remain in service for many years.
The challenge was to identify vulnerabilities (CVE), assess their impact, and deploy security updates efficiently while meeting the EU Cyber Resilience Act requirements.
Our approach
The result
The customer established a scalable process to manage vulnerabilities across long-lifecycle railway products.
By streamlining the path from CVE discovery to deployed security updates, Tria helped improve security visibility, reduce maintenance effort, and strengthen CRA compliance readiness.
Let us know about your product or your challenge and our team will get in touch to discuss how we can help.
Let's TalkYour privacy is important to us.
We use cookies to enhance your experience when visiting our websites: performance cookies show us how you use this website, functional cookies remember your preferences and targeting cookies help us to share content relevant to you. Select "Accept all" for giving your consent to all cookies, select "Cookie settings" for managing the different cookies or select "Reject all" for using only strictly necessary cookies. You can change your cookie settings at any time by clicking on the cookie settings link on the website.